by community-syndication | Sep 19, 2010 | BizTalk Community Blogs via Syndication
The Architecture SIG and the Connected Systems SIG have always had a close relationship and many of the topics have been relevant for both of the groups. In that vein we have decided at this point that because of that close relationship, we have decided to merge the two groups into a single SIG underneath the Architecture SIG name. We will continue to cover Connected Systems topics as these are integral to the .Net Architecture. In addition, we will also start to cover Azure topics at the Architecture SIG as this platform is going to become increasingly important to .Net Architects.
I will co-lead the SIG along with Zoiner Tejada. The user group Website (and calendar) is http://SanDiegoDotNet.com.
The new Architecture SIG will meet on the 2nd Tuesday of the month at the Microsoft Office in La Jolla.
Ironically, earlier today I Tweeted this: Some great quotes/thoughts/truths here (‘Traditional enterprise architecture is dead; long live SOA-inspired EA’ ): http://bit.ly/b0PtYm.
The re-alignment of the SIGs is a good reflection of that!
by community-syndication | Sep 19, 2010 | BizTalk Community Blogs via Syndication
As I will begin doing more posts on and around cloud computing in general, and Windows Azure in particular, I’d first like to give my view on when something is cloud and not.
Why? Well, it’s not the first time a word gets status. It gets hot. It gets overused, overloaded and obfuscated. Vendors, consumers, service providers and others might not always agree what cloud is. It will get slapped on, belted down or fuzzily added to an existing product or service to make it more “today”. I might not agree. Others in turn may think I’m wrong. It will add to the overall confusion. So, to hopefully help provide clarity (but potentially adding to the confusion), when do I consider something to be “cloud”?
There are a couple of characteristics that I would look for when it comes to cloud.
Elastic
Or On-Demand. I would assume that I could scale up and down. At any time. I would assume that the procurement process for another server, piece of service (accounts, users, databases etc) is immediate (or next to). Same when scaling down. I would expect to be able to manage this elasticity myself.
Elasticity is not “I have a cold stand by server I can bring online”. Elasticity is “I need 10, 20, or 100 new instances and I need them for two days”. The dynamic capacity does not have a defined limit.
Pay-per-use
I would expect that the service uses some kind of pay-per-use charge model. How I use the service would be measured. How many hours have I been using it? How many GB of storage? How many MB transferred? How many connections opened? How many customers on boarded? How many users? – That sort of thing.
I would hope not (and this one is on the fence) to have to pay for underlying software in the form of procurement or running licensing. It would be included in the service. However this very much plays to the Software-as-a-Service or Platform-as-a-Service (PaaS) rather that say Infrastructure-as-a-Service (IaaS). In the latter I would of course have to handle licenses myself.
Hardware agnostic
I would expect that I do not need to care about underlying hardware. I wouldn’t need to know the cost of purchasing it nor how it is set-up or configured. I wouldn’t need to specify how my machine is built. Even if I do choose the size of the machine, that’s not really my machine, and I can change that at any time.
I would expect the environment, as far as the service or servers go, to be fault tolerant. If hardware fails, or some service needs to be performed, I would assume it to be transparent to me and not effect me or my service.
Summary
If someone calls their offering a cloud service, and it does not fulfill these things I would think twice before considering it a cloud offering. The service offered might be just what I want and need, but I wouldn’t consider it “cloud”. Windows Azure fulfill all these.
This is not an exhaustive list of what I would expect, nor of the capabilities or limitations of Windows Azure or any other platform, though it is what I would say raises cloud above hosting.
Addendum
The term private cloud is often mentioned by hosting providers that would like to compete (at least marketing wise) with the bigger cloud offerings like Windows Azure. In my experience, localized as it might be, they fulfill some of the tenants I hold to, but they often fail on things like rapid (and self-serviced) procurement of a new resource (like a server) or on the metered pay per use model – where often you are expected to pay for something based on your time of pre-determined need of availability to that resource – like a month, if not a year.
Also, for the something in the cloud to be usable for a business that will likely have parts of their business, but not all of it, in the cloud I would look for it to be
Secure connectivity
Since the cloud is not on-premise I would expect there to be a solution available for how do I, in a secure manner, connect what I almost certainly still have on-premise with what I have off-premise – in the cloud. I would hope this to be based on some kind of federated security model, and not by leasing a land line, using VPN, connecting to the existing Active Directory domain or setting up a trust. Though I’ll settle for tried and proven solution.
Further posts
Continuing on with additional Azure posts I’ll try and link back to these pillars, if possible. With pure how-to technology posts that might not always be applicable, but keep these base concepts in mind anyway so that you architect and build your solutions to support them.
by community-syndication | Sep 18, 2010 | BizTalk Community Blogs via Syndication
A few hours ago we released a Microsoft Security Advisory about a security vulnerability in ASP.NET. This vulnerability exists in all versions of ASP.NET.
This vulnerability was publically disclosed late Friday at a security conference. We recommend that all customers immediately apply a workaround (described below) to prevent attackers from using this vulnerability against your ASP.NET applications.
What does the vulnerability enable?
An attacker using this vulnerability can request and download files within an ASP.NET Application like the web.config file (which often contains sensitive data).
At attacker exploiting this vulnerability can also decrypt data sent to the client in an encrypted state (like ViewState data within a page).
How the Vulnerability Works
To understand how this vulnerability works, you need to know about cryptographic oracles. An oracle in the context of cryptography is a system which provides hints as you ask it questions. In this case, there is a vulnerability in ASP.NET which acts as a padding oracle. This allows an attacker to send cipher text to the web server and learn if it was decrypted properly by examining which error code was returned by the web server. By making many such requests (and watching what errors are returned) the attacker can learn enough to successfully decrypt the rest of the cipher text.
How to Workaround The Vulnerability
A workaround you can use to prevent this vulnerability is to enable the <customErrors> feature of ASP.NET, and explicitly configure your applications to always return the same error page – regardless of the error encountered on the server. By mapping all error pages to a single error page, you prevent a hacker from distinguishing between the different types of errors that occur on a server.
Important: It is not enough to simply turn on CustomErrors or have it set to RemoteOnly. You also need to make sure that all errors are configured to return the same error page. This requires you to explicitly set the “defaultRedirect” attribute on the <customErrors> section and ensure that no per-status codes are set.
Enabling the Workaround on ASP.NET V1.0 to V3.5
If you are using ASP.NET 1.0, ASP.NET 1.1, ASP.NET 2.0, or ASP.NET 3.5 then you should follow the below steps to enable <customErrors> and map all errors to a single error page:
1) Edit your ASP.NET Application’s root Web.Config file. If the file doesn’t exist, then create one in the root directory of the application.
2) Create or modify the <customErrors> section of the web.config file to have the below settings:
<configuration>

   <system.web>

      <customErrors mode="On" defaultRedirect="~/error.html" />

   </system.web>

</configuration>
.csharpcode, .csharpcode pre
{
font-size: small;
color: black;
font-family: consolas, “Courier New”, courier, monospace;
background-color: #ffffff;
/*white-space: pre;*/
}
.csharpcode pre { margin: 0em; }
.csharpcode .rem { color: #008000; }
.csharpcode .kwrd { color: #0000ff; }
.csharpcode .str { color: #006080; }
.csharpcode .op { color: #0000c0; }
.csharpcode .preproc { color: #cc6633; }
.csharpcode .asp { background-color: #ffff00; }
.csharpcode .html { color: #800000; }
.csharpcode .attr { color: #ff0000; }
.csharpcode .alt
{
background-color: #f4f4f4;
width: 100%;
margin: 0em;
}
.csharpcode .lnum { color: #606060; }
.csharpcode, .csharpcode pre
{
font-size: small;
color: black;
font-family: consolas, “Courier New”, courier, monospace;
background-color: #ffffff;
/*white-space: pre;*/
}
.csharpcode pre { margin: 0em; }
.csharpcode .rem { color: #008000; }
.csharpcode .kwrd { color: #0000ff; }
.csharpcode .str { color: #006080; }
.csharpcode .op { color: #0000c0; }
.csharpcode .preproc { color: #cc6633; }
.csharpcode .asp { background-color: #ffff00; }
.csharpcode .html { color: #800000; }
.csharpcode .attr { color: #ff0000; }
.csharpcode .alt
{
background-color: #f4f4f4;
width: 100%;
margin: 0em;
}
.csharpcode .lnum { color: #606060; }
.csharpcode, .csharpcode pre
{
font-size: small;
color: black;
font-family: consolas, “Courier New”, courier, monospace;
background-color: #ffffff;
/*white-space: pre;*/
}
.csharpcode pre { margin: 0em; }
.csharpcode .rem { color: #008000; }
.csharpcode .kwrd { color: #0000ff; }
.csharpcode .str { color: #006080; }
.csharpcode .op { color: #0000c0; }
.csharpcode .preproc { color: #cc6633; }
.csharpcode .asp { background-color: #ffff00; }
.csharpcode .html { color: #800000; }
.csharpcode .attr { color: #ff0000; }
.csharpcode .alt
{
background-color: #f4f4f4;
width: 100%;
margin: 0em;
}
.csharpcode .lnum { color: #606060; }
3) You can then add an error.html file to your application that contains an appropriate error page of your choosing (containing whatever content you like). This file will be displayed anytime an error occurs within the web application.
Notes: The important things to note above is that customErrors is set to “on”, and that all errors are handled by the defaultRedirect error page. There are not any per-status code error pages defined – which means that there are no <error> sub-elements within the <customErrors> section. This avoids an attacker being able to differentiate why an error occurred on the server, and prevents information disclosure.
Enabling the Workaround on ASP.NET V3.5 SP1 and ASP.NET 4.0
If you are using ASP.NET 3.5 SP1 or ASP.NET 4.0 then you should follow the below steps to enable <customErrors> and map all errors to a single error page:
1) Edit your ASP.NET Application’s root Web.Config file. If the file doesn’t exist, then create one in the root directory of the application.
2) Create or modify the <customErrors> section of the web.config file to have the below settings. Note the use of redirectMode=”ResponseRewrite” with .NET 3.5 SP1 and .NET 4.0:
<configuration>

   <system.web>

     <customErrors mode="On" redirectMode="ResponseRewrite" defaultRedirect="~/error.aspx" />

   </system.web>

</configuration>
.csharpcode, .csharpcode pre
{
font-size: small;
color: black;
font-family: consolas, “Courier New”, courier, monospace;
background-color: #ffffff;
/*white-space: pre;*/
}
.csharpcode pre { margin: 0em; }
.csharpcode .rem { color: #008000; }
.csharpcode .kwrd { color: #0000ff; }
.csharpcode .str { color: #006080; }
.csharpcode .op { color: #0000c0; }
.csharpcode .preproc { color: #cc6633; }
.csharpcode .asp { background-color: #ffff00; }
.csharpcode .html { color: #800000; }
.csharpcode .attr { color: #ff0000; }
.csharpcode .alt
{
background-color: #f4f4f4;
width: 100%;
margin: 0em;
}
.csharpcode .lnum { color: #606060; }
.csharpcode, .csharpcode pre
{
font-size: small;
color: black;
font-family: consolas, “Courier New”, courier, monospace;
background-color: #ffffff;
/*white-space: pre;*/
}
.csharpcode pre { margin: 0em; }
.csharpcode .rem { color: #008000; }
.csharpcode .kwrd { color: #0000ff; }
.csharpcode .str { color: #006080; }
.csharpcode .op { color: #0000c0; }
.csharpcode .preproc { color: #cc6633; }
.csharpcode .asp { background-color: #ffff00; }
.csharpcode .html { color: #800000; }
.csharpcode .attr { color: #ff0000; }
.csharpcode .alt
{
background-color: #f4f4f4;
width: 100%;
margin: 0em;
}
.csharpcode .lnum { color: #606060; }
3) You can then add an Error.aspx to your application that contains an appropriate error page of your choosing (containing whatever content you like). This file will be displayed anytime an error occurs within the web application.
4) We recommend adding the below code to the Page_Load() server event handler within the Error.aspx file to add a random, small sleep delay. This will help to further obfuscate errors.
VB Version
Below is a VB version of an Error.aspx file that you can use, and which has a random, small sleep delay in it. You do not need to compile this into an application – you can optionally just save this Error.aspx file into the application directory on your web-server:
<%@ Page Language="VB" AutoEventWireup="true" %>
<%@ Import Namespace="System.Security.Cryptography" %>
<%@ Import Namespace="System.Threading" %>

<script runat="server">
    Sub Page_Load()
        Dim delay As Byte() = New Byte(0) {}
        Dim prng As RandomNumberGenerator = New RNGCryptoServiceProvider()

        prng.GetBytes(delay)
        Thread.Sleep(CType(delay(0), Integer))

        Dim disposable As IDisposable = TryCast(prng, IDisposable)
        If Not disposable Is Nothing Then
            disposable.Dispose()
        End If
    End Sub
</script>

<html>
<head runat="server">
    <title>Error</title>
</head>
<body>
    <div>
        Sorry - an error occured
    </div>
</body>
</html>
.csharpcode, .csharpcode pre
{
font-size: small;
color: black;
font-family: consolas, “Courier New”, courier, monospace;
background-color: #ffffff;
/*white-space: pre;*/
}
.csharpcode pre { margin: 0em; }
.csharpcode .rem { color: #008000; }
.csharpcode .kwrd { color: #0000ff; }
.csharpcode .str { color: #006080; }
.csharpcode .op { color: #0000c0; }
.csharpcode .preproc { color: #cc6633; }
.csharpcode .asp { background-color: #ffff00; }
.csharpcode .html { color: #800000; }
.csharpcode .attr { color: #ff0000; }
.csharpcode .alt
{
background-color: #f4f4f4;
width: 100%;
margin: 0em;
}
.csharpcode .lnum { color: #606060; }
C# Version
Below is a C# version of an Error.aspx file that you can use, and which has a random, small sleep delay in it. You do not need to compile this into an application – you can optionally just save it into the application directory on your web-server:
<%@ Page Language="C#" AutoEventWireup="true" %>
<%@ Import Namespace="System.Security.Cryptography" %>
<%@ Import Namespace="System.Threading" %>

<script runat="server">
   void Page_Load() {
      byte[] delay = new byte[1];
      RandomNumberGenerator prng = new RNGCryptoServiceProvider();

      prng.GetBytes(delay);
      Thread.Sleep((int)delay[0]);

      IDisposable disposable = prng as IDisposable;
      if (disposable != null) { disposable.Dispose(); }
    }
</script>

<html>
<head runat="server">
    <title>Error</title>
</head>
<body>
    <div>
        An error occurred while processing your request.
    </div>
</body>
</html>
.csharpcode, .csharpcode pre
{
font-size: small;
color: black;
font-family: consolas, “Courier New”, courier, monospace;
background-color: #ffffff;
/*white-space: pre;*/
}
.csharpcode pre { margin: 0em; }
.csharpcode .rem { color: #008000; }
.csharpcode .kwrd { color: #0000ff; }
.csharpcode .str { color: #006080; }
.csharpcode .op { color: #0000c0; }
.csharpcode .preproc { color: #cc6633; }
.csharpcode .asp { background-color: #ffff00; }
.csharpcode .html { color: #800000; }
.csharpcode .attr { color: #ff0000; }
.csharpcode .alt
{
background-color: #f4f4f4;
width: 100%;
margin: 0em;
}
.csharpcode .lnum { color: #606060; }
How to Verify if the Workaround is Enabled
Once you have applied the above workaround, you can test to make sure the <customErrors> section is correctly configured by requesting a URL like this from your site: http://mysite.com/pagethatdoesnotexist.aspx
If you see the custom error page appear (because the file you requested doesn’t exist) then your configuration should be setup correctly. If you see a standard ASP.NET error then it is likely that you missed one of the steps above. To see more information about what might be the cause of the problem, you can try setting <customErrors mode=”remoteOnly”/> – which will enable you to see the error message if you are connecting to the site from a local browser.
How to Find Vulnerable ASP.NET Applications on Your Web Server
We have published a .vbs script that you can save and run on your web-server to determine if there are ASP.NET applications installed on it that either have <customErrors> turned off, or which differentiate error messages depending on status codes.
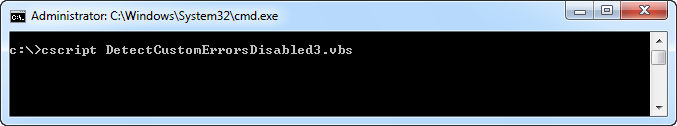
You can download the .vbs script here. Simply copy/paste the script into a text file called “DetectCustomErrors.vbs” and save it to disk. Then launch a command window that is elevated as admin and run “cscript DetectCustomErrors.vbs” to run it against your local web-server. It will enumerate all of the applications within your web server and verify that the correct <customErrors> configuration has been specified.
It will flag any application where it finds that an application’s web.config file doesn’t have the <customErrors> section (in which case you need to add it), or doesn’t have it set correctly to workaround this attack (in which case you need to update it). It will print “ok” for each application web.config file it finds that is fine. This should hopefully make it easier to locate issues.
Note: We have developed this detection script over the last few hours, and will be refining it further in the future. I will post an update in this section each time we make a change to it.
How to Find More Information about this Vulnerability
You can learn more about this vulnerability from:
Forum for Questions
We have setup a dedicated forum on the www.asp.net site to help answer questions about this vulnerability.
Post questions here to ask questions and get help about this vulnerability.
Summary
We will post more details as we learn more, and will also be releasing a patch that can be used to correct the root cause of the issue (and avoid the need for the above workaround).
Until then, please apply the above workaround to all of your ASP.NET applications to prevent attackers from exploiting it.
Thanks,
Scott
by community-syndication | Sep 17, 2010 | BizTalk Community Blogs via Syndication
Windows Server AppFabric Monitoring works with Oracle (10g XE) database?
Yes, indeed! AppFabric Monitoring Provider extensibility is proven out in this MSDN Code Gallery Release – http://code.msdn.microsoft.com/AFMonitoringOracleDB
The release includes the Visual Studio 2010 solution that contains all the relevant SQL and .NET source used to support the Windows Server AppFabric Monitoring Schema. Also included is the implementation guide (AppFabricMonitoringOnOracle10gXE.docx) and this document provides adequate elaboration on: AppFabric Monitoring basics; setup; database schema; implementation; and finally the UI pieces. For the convenience of the developers this document is also included with this post.
Figure 1: Snapshot of Solution/VS Project in the Release.
The two screenshots below demonstrate the comprehensive implementation.
Figure 2: Selecting the Oracle Provider for AppFabric Monitoring functionality
Figure 3: Monitoring Data extracted from Oracle Database.
Namaste!



